Category: Purple Team
-
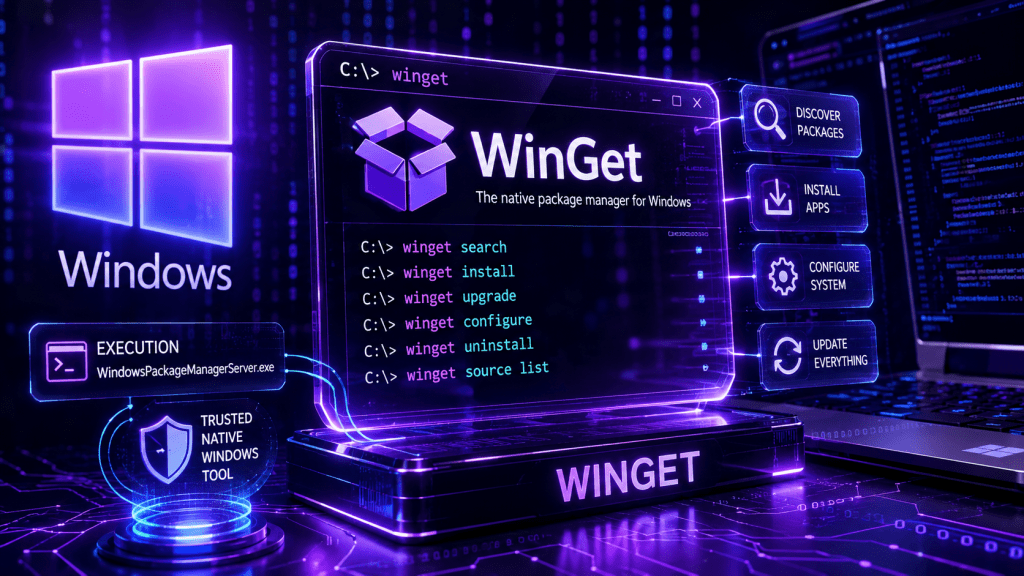
WinGet
WinGet also known as Windows Package Manager, is Microsoft’s command-line for discovering, installing, upgrading, configuring, and removing applications on Windows. It is commonly used by Administrators and developers to automate software deployment and system setup. However, it can be abused to proxy execution and evade detection. Threat actors can execute…
-
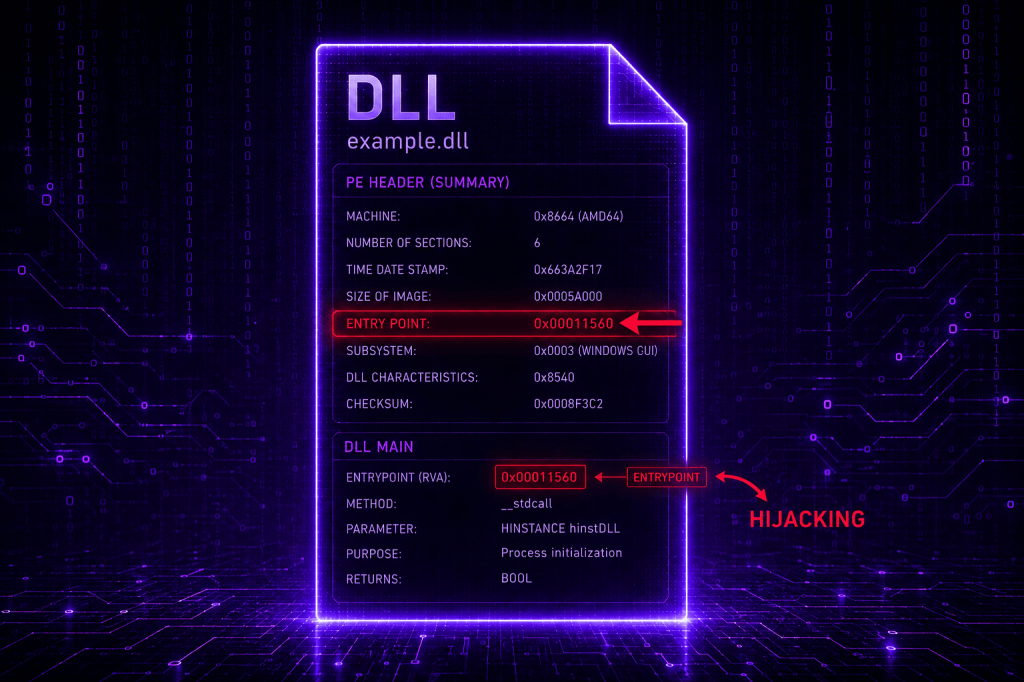
EntryPoint Hijacking
The technique of EntryPoint Hijacking introduces a stealthier approach to code injection, as it doesn’t rely on API calls that create a new thread within the process context, and it is independent of the attack chain. Arbitrary code is written to memory, but it executes only when the process legitimately…
-
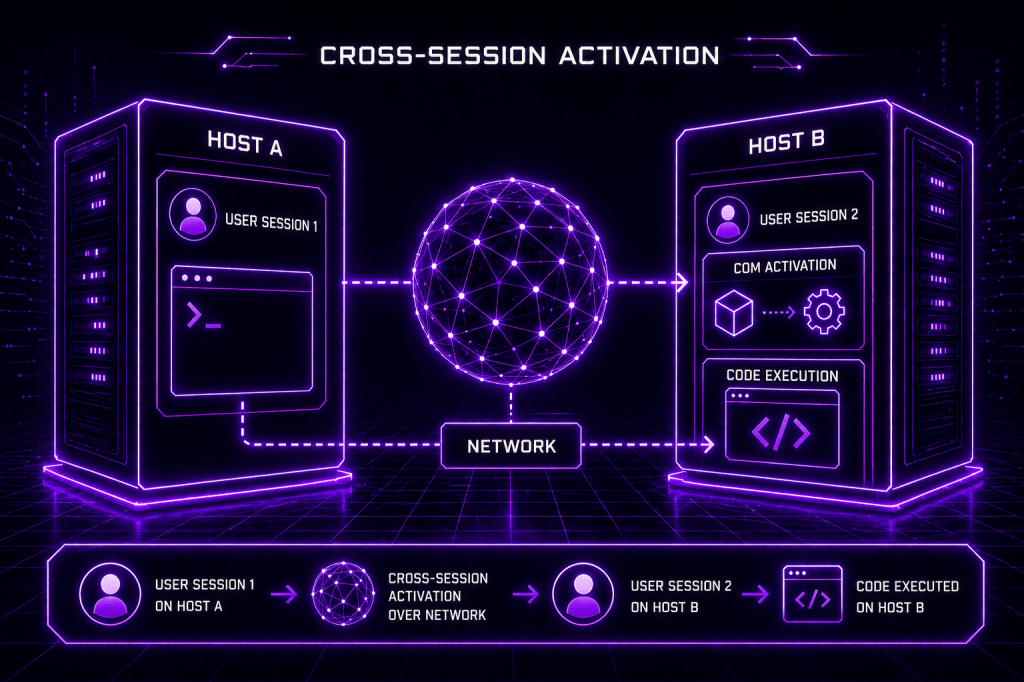
Cross-Session Activation
Traditional lateral movement techniques are no longer applicable in the modern era due to developments in the detection capability by most of the EDR vendors. Techniques that abuse legitimate Windows functionality, such as COM, has always been in the interest of adversaries. Cross-Session activation (CSA) is considered the latest evolution…
-
Microsoft Speech
SpeechRuntime is a legitimate Windows component that supports Microsoft’s speech-related capabilities, including voice input and speech recognition features used across modern Windows experiences. The SpeechRuntime.exe binary is linked to the Microsoft speech framework. However, threat actors with elevated privileges can move laterally by executing code under the context of the…

